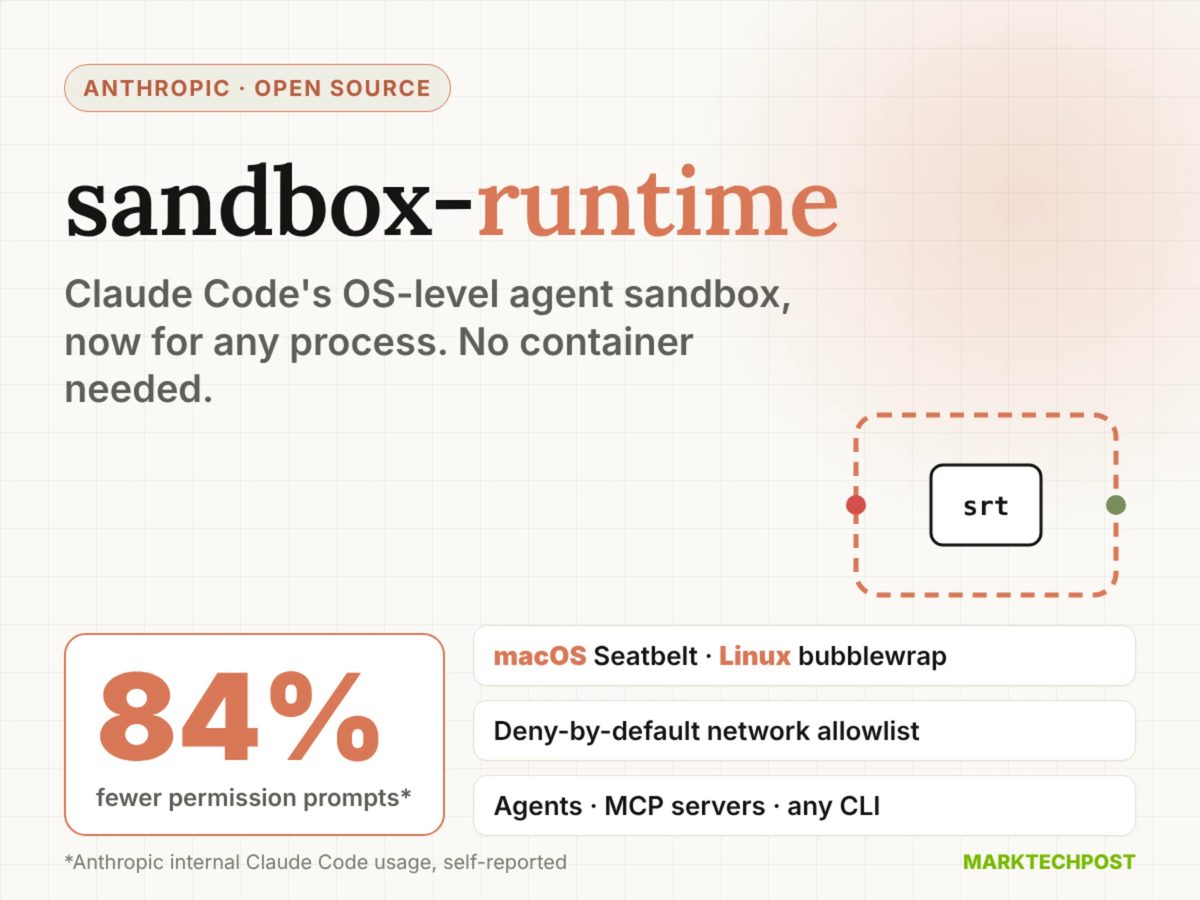
Anthropic has open-sourced its sandbox-runtime (srt), an OS-level isolation tool that powers the sandboxed bash environment in Claude Code. The CLI and TypeScript library wraps any process in strict filesystem and network boundaries without requiring containerization. It leverages native OS primitives on Linux and macOS, routing external traffic through local HTTP and SOCKS5 proxies while restricting file write access by default.
The tool is designed to work across custom AI agents, local Model Context Protocol (MCP) servers, and command-line programs. According to Anthropic, implementing this sandboxing reduced permission prompts by 84% in internal Claude Code testing by minimizing developer approval fatigue. Developers can configure file and network allowlists globally or per project.
Why it matters
Enables secure execution of autonomous coding agents locally without the heavy overhead of Docker or virtual machines.
Reduces developer approval fatigue by enforcing predefined filesystem and domain guardrails.
Provides a standardized TypeScript library for securing third-party Model Context Protocol (MCP) servers.
Source: marktechpost.com