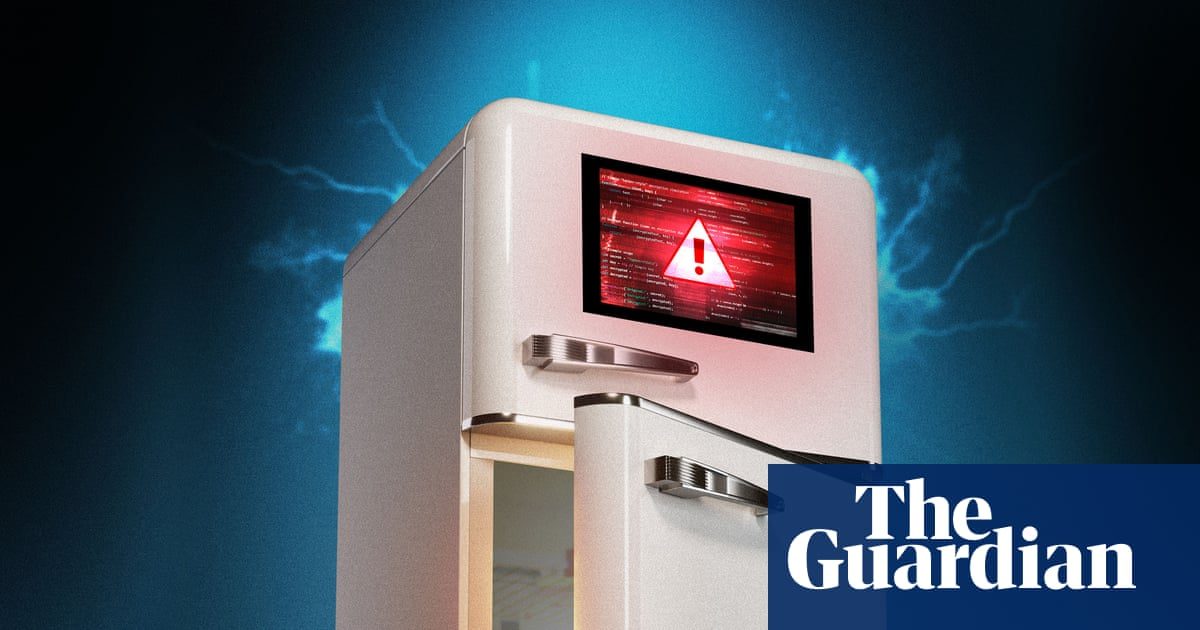
A series of severe cyberattacks disrupted international businesses and digital infrastructure last week, escalating fears of a widespread hacking trend. European retailers, blood banks, and wholesale operators experienced compromised internet-connected refrigeration systems that forced temperatures to spike dramatically. The incidents occurred alongside a $6.3 billion theft from cryptocurrency exchange Binance on October 30 and a hijacked emergency alert app in Ukraine that broadcasted fake nuclear strike warnings on November 1.
Cybersecurity experts and official bodies attribute the rising frequency and severity of breaches to a combination of geopolitical tensions and advanced AI technologies. According to the UK’s National Cyber Security Centre (NCSC), AI tools are increasingly enabling attackers to discover software vulnerabilities, scout targets, and write malicious code at scale. NCSC leadership warned that high-volume security incidents will continue to rise rapidly as systemic IT vulnerabilities are exposed by automated tools.
Industry observers have drawn parallels between recent automated vulnerability discoveries and major systemic shocks, noting that public-facing systems remain exposed. The NCSC projected that by 2028, AI-powered malicious software is highly likely to target critical national infrastructure, including power stations, airports, and healthcare facilities.
Why it matters
Enterprise security teams must prepare for an increased volume of automated exploits driven by AI-discovered system vulnerabilities.
Hardware and IoT operators face heightened operational risks as physical infrastructure connected to networks becomes a target for automated cyberattacks.
Founders developing defense and security tools have immediate market opportunities in AI-assisted threat detection and automated patch deployment.
Source: theguardian.com