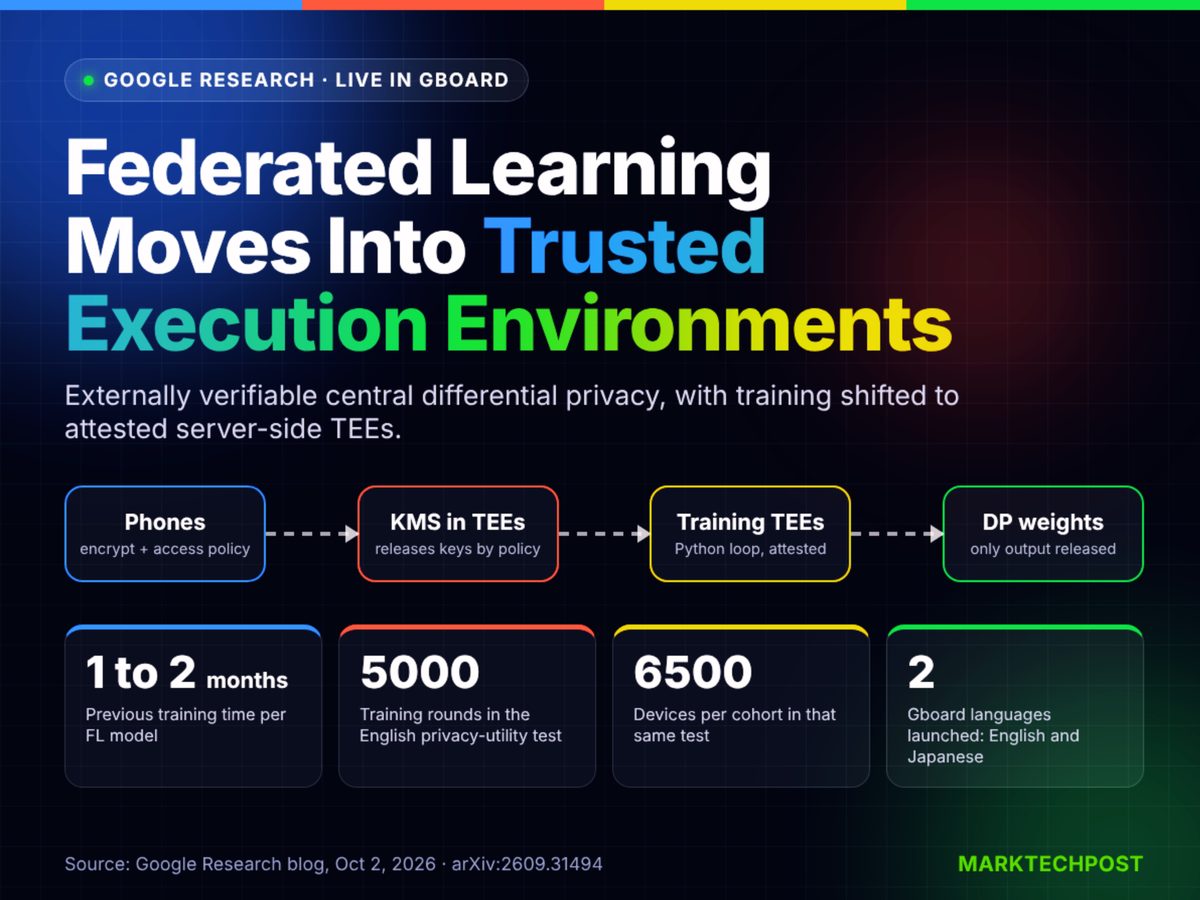
Google Research has deployed a new Federated Learning system that combines Trusted Execution Environments (TEEs) with externally verifiable central differential privacy (DP). The upgraded architecture has been implemented on Gboard to train English and Japanese next-word prediction models while offering mathematical privacy guarantees alongside improved accuracy, according to a research paper published by the team.
The system addresses privacy verification limitations inherent in earlier Federated Learning frameworks launched in 2017. By moving client gradient computations to attestable server-side TEEs and publishing access policies to Rekor—Sigstore’s public transparency log—external auditors can verify that data processing binaries and Key Management System logic are built reproducibly from open-source code without inspecting underlying raw user data.
Why it matters
Enables enterprise AI teams to implement verifiable, privacy-preserving model training on client devices without requiring user trust in the central operator.
Provides a reproducible architecture for combining Trusted Execution Environments with state-of-the-art matrix factorization differential privacy algorithms.
Source: marktechpost.com