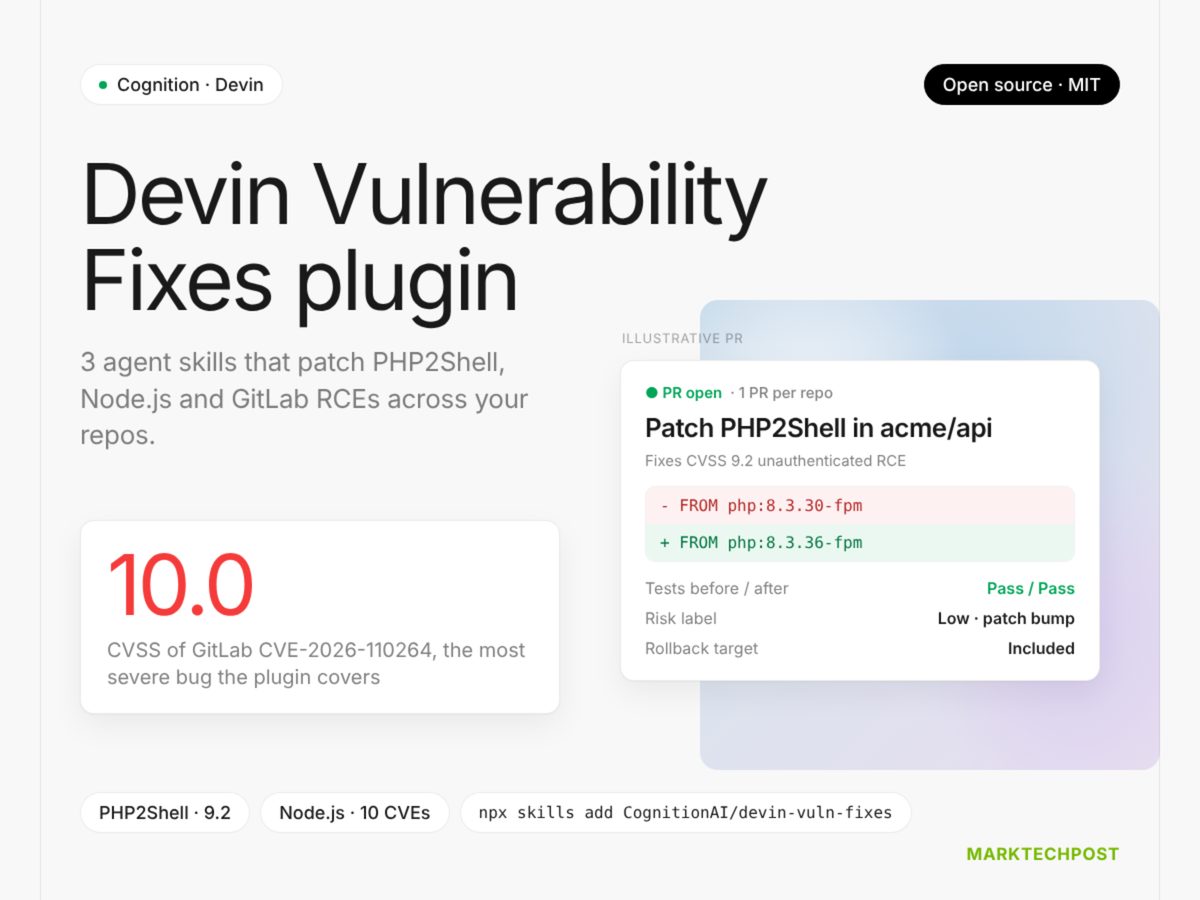
AI startup Cognition has open-sourced the Devin Vulnerability Fixes plugin, offering automated remediation workflows for three recent critical remote code execution (RCE) advisories. The plugin targets infrastructure vulnerabilities in PHP2Shell, recent Node.js updates, and a maximum-severity CVSS 10.0 bug in self-managed GitLab instances.
Unlike traditional tools that patch application dependencies, Cognition’s plugin operates at the runtime layer by identifying and fixing base container images, operating system packages, and infrastructure-as-code files. The skills follow an automated five-step process that inventories systems, generates targeted patches, conducts automated testing, and submits pull requests.
The tool is available under the MIT license and can be executed via Devin, Claude Code, or any coding agent supporting the open SKILL.md format.
Why it matters
Extends autonomous coding agents beyond basic source code editing into infrastructure and runtime security remediation.
Reduces manual patch management overhead for DevOps and security engineering teams.
Demonstrates standardized interoperability for AI agent skill definitions across competing developer tools.
Source: marktechpost.com