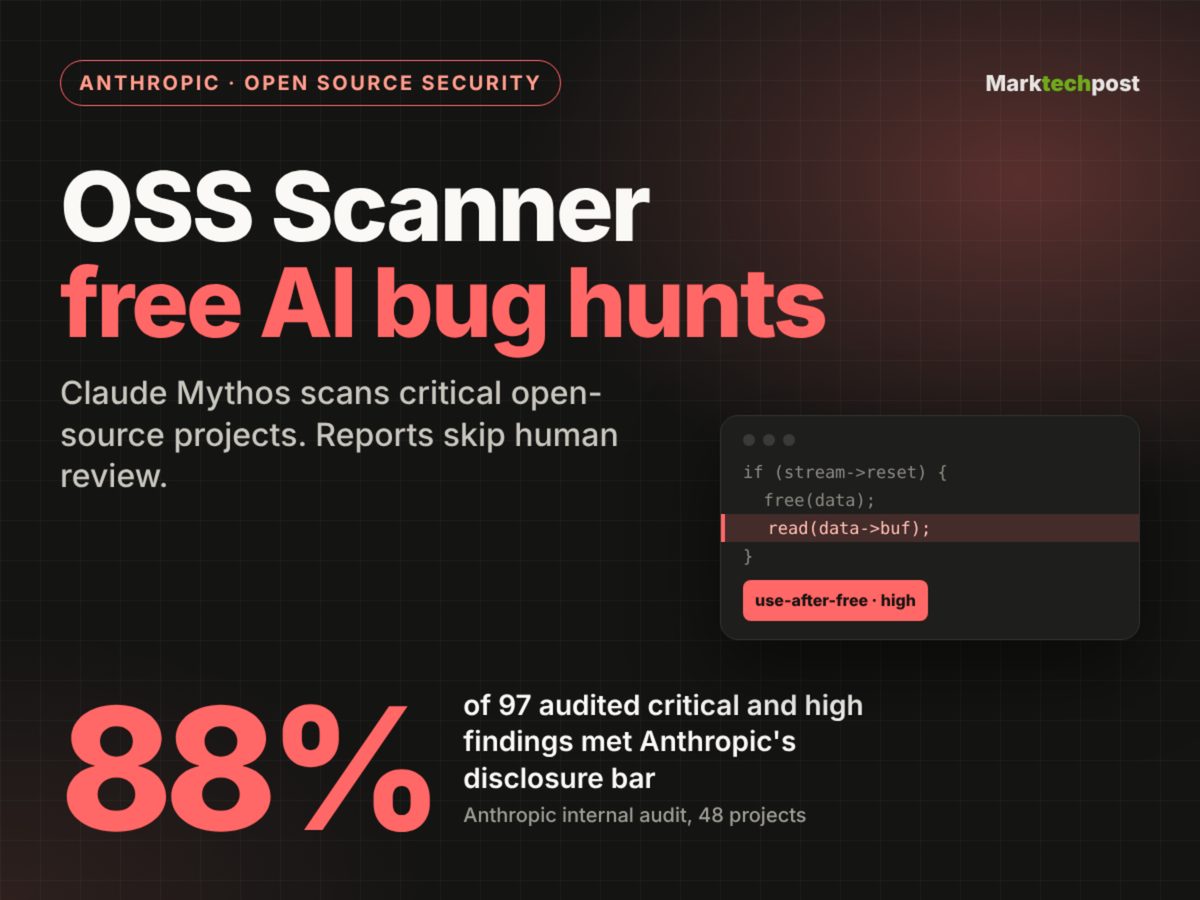
Anthropic has released OSS Scanner, a free, opt-in program that continuously audits open-source codebases for security vulnerabilities. Run jointly by Anthropic’s Frontier Red Team and Safeguards Research team, the tool leverages the company’s frontier models, including Claude Mythos, to automatically perform static analysis, root cause analysis, and candidate patch generation for enrolled projects.
The service operates by isolating code execution within network-restricted virtual machines after fetching dependencies. Findings are delivered directly to repository maintainers without prior human review from Anthropic. Within 11 days of its initial launch, the program uncovered 77 critical and 803 high model-rated vulnerabilities across participating codebases, including verified CVEs in major projects like wolfSSL and curl.
While the direct delivery model speeds up bug discovery, it places the burden of triaging automated reports onto open-source maintainers. The initiative reflects broader improvements in LLM capability, with models finding over 85% of vulnerabilities on security benchmarks like CyberGym.
Why it matters
Automates critical security audits for open-source dependencies, helping engineering teams catch severe zero-day bugs faster.
Shifts triage workload directly to maintainers, creating potential operational noise alongside valid vulnerability reports.
Demonstrates practical enterprise applications of frontier LLMs in automated software engineering and cybersecurity.
Source: marktechpost.com