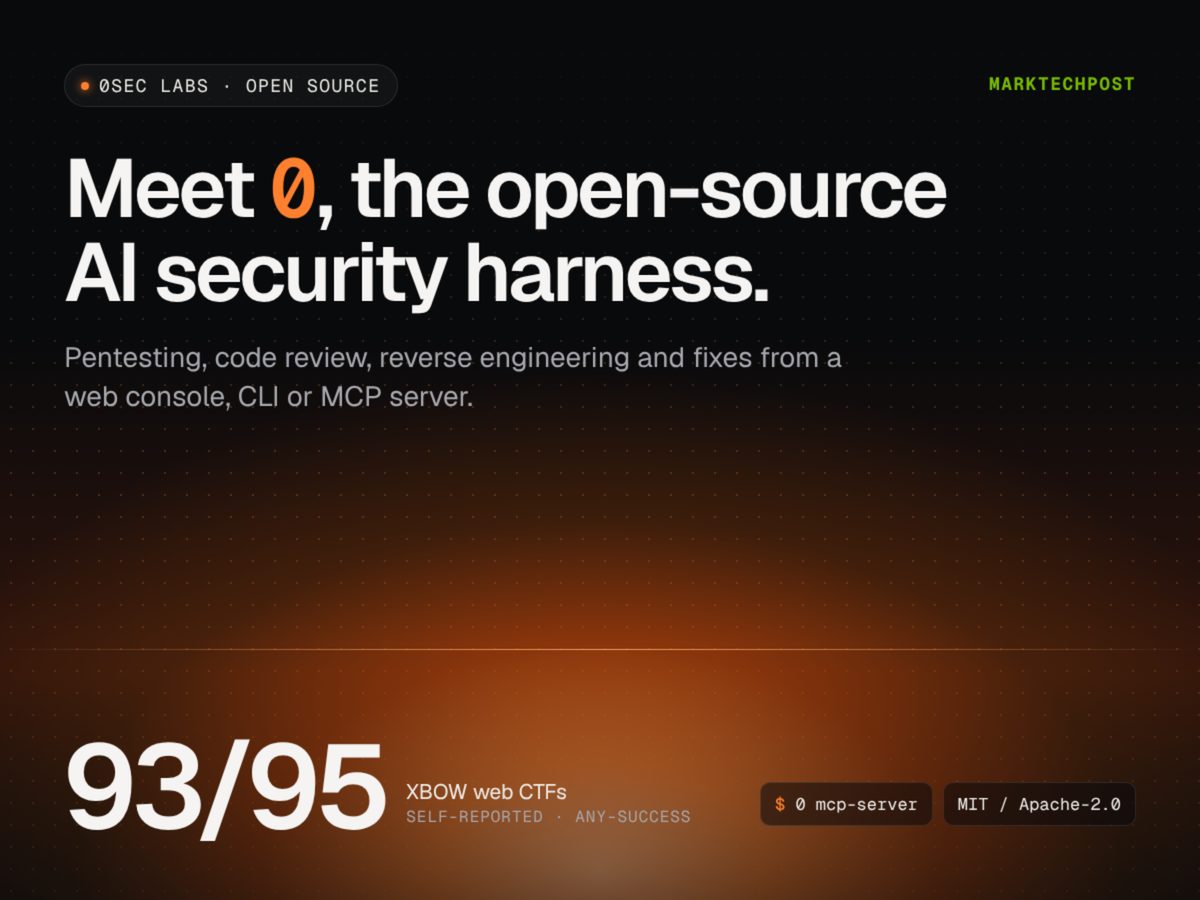
Y Combinator-backed startup 0sec Labs has released 0, an open-source, dual-licensed (MIT/Apache-2.0) AI security harness available as a research preview. Operating as a model-agnostic control plane, 0 automates code review, web penetration testing, reverse engineering, and automated patch creation using a local browser UI, CLI, or MCP server integration.
The framework connects to external model providers via API keys—supporting OpenAI, Anthropic, DeepSeek, and local CLI runtimes—and executes shell-first security testing workflows. According to 0sec Labs, the system successfully identified over 30 zero-day vulnerabilities in the Linux kernel and various open-source software libraries during research testing.
Why it matters
DevSecOps teams can deploy open-source agentic harnesses to automate root-cause vulnerability analysis and patch creation locally.
Model-agnostic control planes utilizing the Model Context Protocol (MCP) enable seamless integration into existing developer CLI toolchains.
Source: marktechpost.com